
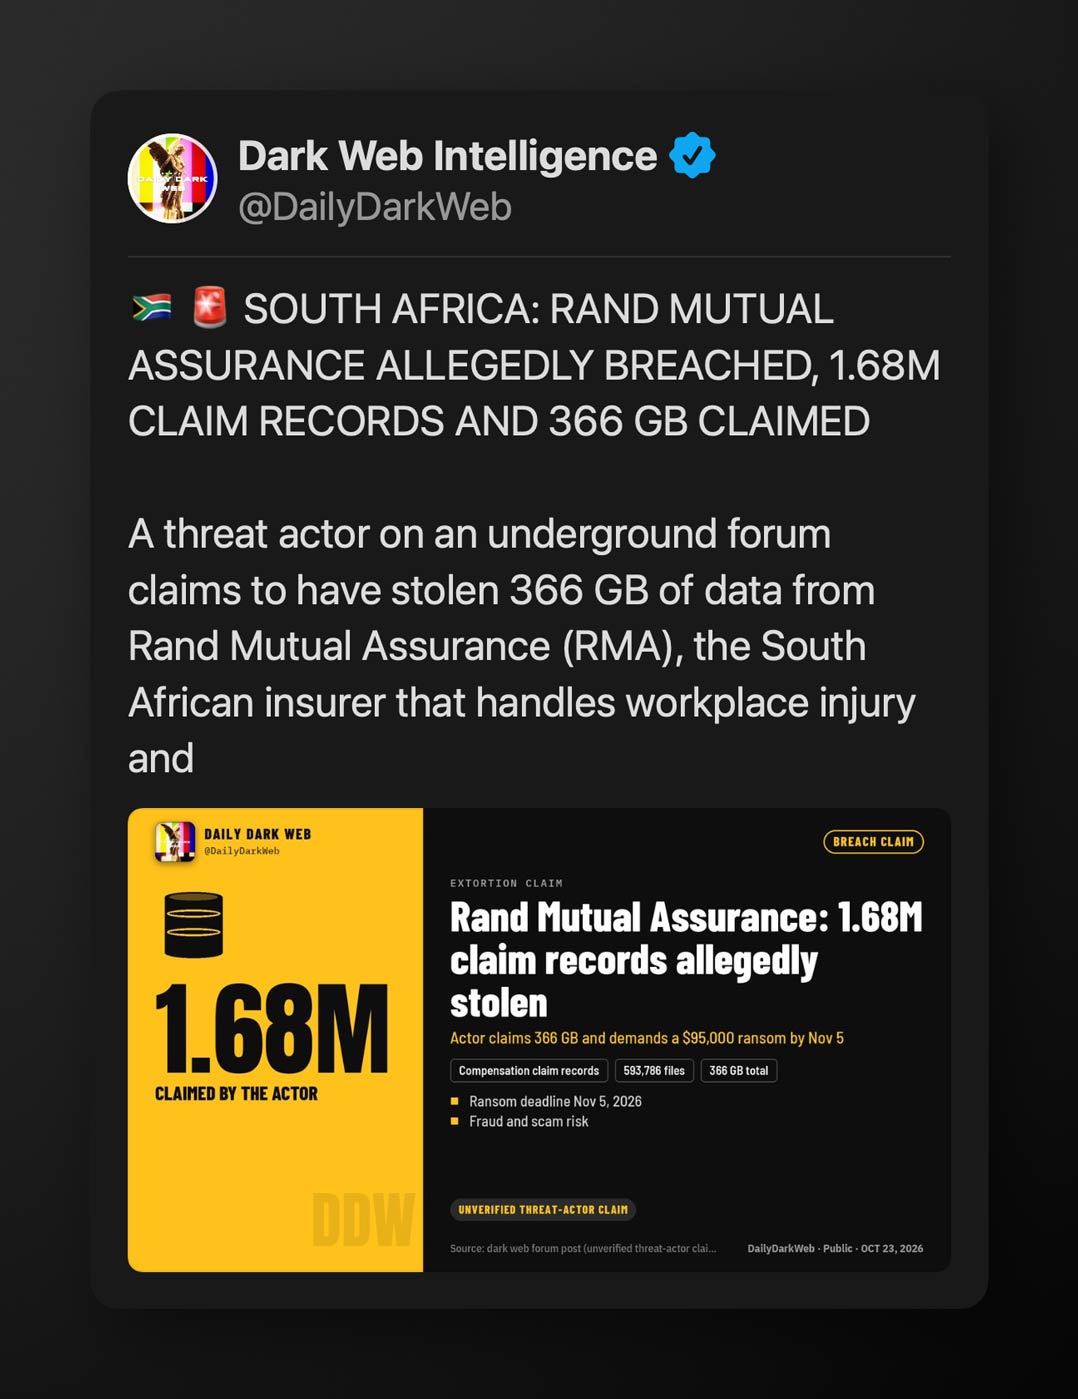
Rand Mutual Assurance (RMA), which handles workplace injury and disease claims for South Africa’s mining and metals industries, is investigating a claimed data breach. A hacker says it has stolen 1.68 million compensation claim records and is demanding a US$95 000 (R1.6-million) ransom.
RMA “has received an alert about a data breach” and “investigations are under way”, Nduduzo Majozi, RMA’s chief information security officer, said in a statement shared with TechCentral on Friday. The company will communicate further once the investigations are concluded, Majozi said.
The statement does not confirm that any data was taken, and it does not address the ransom demand.
The claims were made on an underground forum and reported on Friday by Dark Web Intelligence, an account on X that tracks such forums. The attacker says it holds 366GB of data, including 1.68 million claim records and 593 786 files. It has set a deadline of 5 November for payment, after which it says it will release the data. Dark Web Intelligence describes the claims as unverified, and TechCentral has not seen the forum post or any sample data.
…article continues below…
A count of records is not a count of people. When a hacker claimed this month to have taken 80 million records from pathology group Ampath, the company said the figure referred to database entries, not individual patients.
RMA was founded in 1894 and is licensed under the Compensation for Occupational Injuries and Diseases Act to administer compensation for the mining industry and, since 2015, for iron, steel and metal employers. Those employers register with RMA rather than with the state’s Compensation Fund. Compensation claims can contain a worker’s ID number, medical reports on an injury or illness and bank details for payment.
The claim follows a run of attacks on South African insurers and healthcare companies. The ransomware group behind June’s breach at software supplier MIP Holdings, whose CEO said data belonging to customers of about 45 insurers was taken, has since listed LegalWise, Samwumed and Edcon on its leak site.
The Protection of Personal Information Act (Popia) requires an organisation to notify the Information Regulator and the people affected as soon as reasonably possible when there are reasonable grounds to believe their personal information has been accessed by an unauthorised person. — © 2026 NewsCentral Media

